

Anthropic OSS Scanner: build a maintainer triage boundary before enrolling
Anthropic’s opt-in OSS Scanner sends model-generated findings. Review eligibility, offline audit boundaries and the human decisions between a report and a release.
Underlying source event: 2026-10-08. Rangoon publication: October 10, 2026. Source facts and independent operator analysis remain distinct; no integration or endorsement implied.
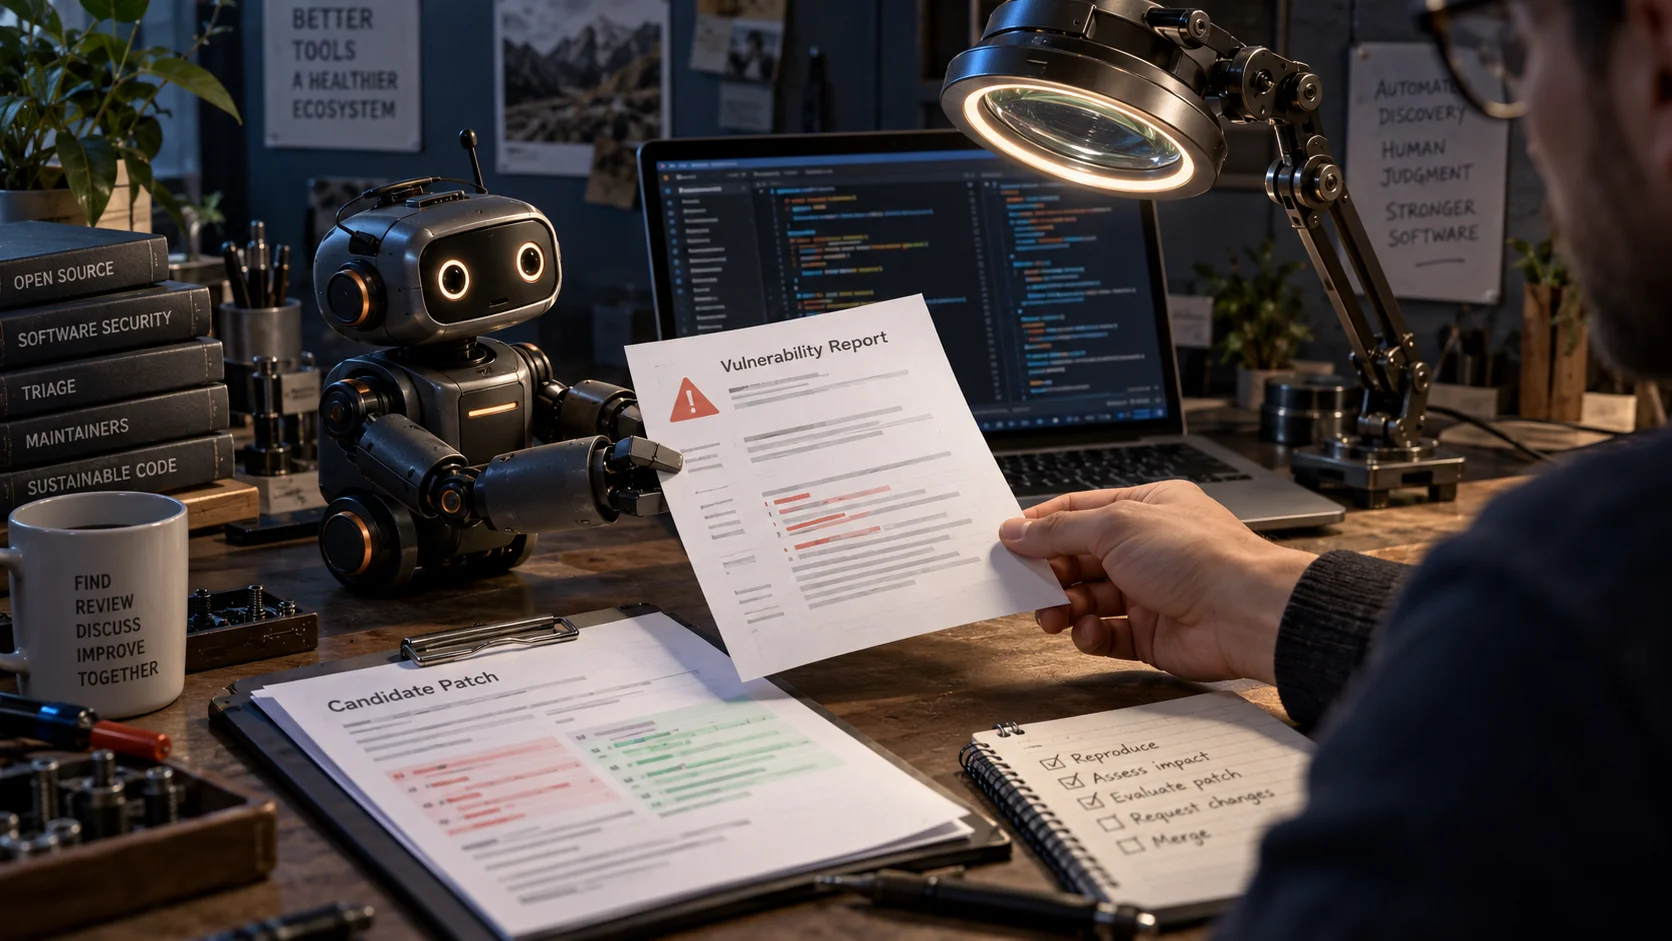
Key takeaways
- Opt-in scanning produces candidate findings, not human-approved releases.
- Networked image builds and offline audits are distinct boundaries.
- Assign triage capacity and release authority before adding another automated reporter.
What the service provides[source 1][source 3]
Anthropic announced OSS Scanner on October 8 as an opt-in, no-cost service for eligible open-source projects. It sends periodic security findings produced by models without human review or triage. Reports include a reproducer, an explanation and a candidate patch when available. Maintainers should treat those outputs as submissions for investigation, rather than confirmed vulnerabilities or approved changes.
The scanner sits within the new Anthropic Cyber Mission alongside a separate critical-infrastructure program. The announcement does not establish that every project can enroll, that findings are error-free, or that any suggested patch is safe to ship. This article focuses on the maintainer workflow, not on claims about the effectiveness of industrial deployments.
Eligibility and the build boundary[source 2]
The FAQ describes case-by-case eligibility for established projects important to infrastructure and user security. Anthropic manually confirms core-maintainer identity. Enrollment uses a pull request adding project configuration to its public scanner repository. The documented configuration identifies the repository, primary contact and build environment; optional fields include a threat model, encrypted-report key and a disabled switch.
A significant technical distinction is that the Dockerfile build has network access, while the subsequent audit runs offline. The FAQ recommends checking that the container builds and tests pass. Offline auditing does not mean the preceding dependency installation was isolated from the network, and it does not prove that a proposed fix behaves correctly in the deployed environment.
Analysis: separate submission, verification and release[source 1][source 2]
A maintainer can organize incoming reports into three distinct records: what the scanner submitted, what the team reproduced, and what the release owner accepted. Preserve the reported revision and reproducer before modifying either. Record the observed result separately from the model’s severity label. A crash in a test environment may be real while its claimed production impact depends on an assumption the project does not share.
Candidate patches deserve the same review as other external contributions. Run the relevant regression tests, inspect changes to authentication and resource handling, and test the original failure against the proposed fix. Avoid giving a report-processing agent permission to merge or publish merely because it can read the report. A correct reproduction and a safe release are separate decisions with different evidence.
These are engineering recommendations, not additional Anthropic enrollment requirements. Teams can use a small queue with explicit states such as received, reproduced, duplicate, rejected and accepted for release. Each transition should name an accountable maintainer and retain the evidence used. Uncertainty should remain visible when a reproducer cannot run or the affected configuration is unknown.
Analysis: plan for report volume and sensitive evidence[source 2]
Before enrolling, assign someone to receive reports and establish a private handling path for exploit details. Choose how duplicates, incomplete reproductions and disputed severity will be handled. Track response capacity rather than interpreting the number of reports as the number of confirmed defects. If submissions exceed capacity, reducing intake is more useful than creating a backlog that nobody can validate.
Threat-model guidance can explain supported deployments, untrusted inputs and excluded assumptions. It gives the scanner context, but should not be treated as an authorization mechanism for unrelated tool calls. Keep credentials and production data out of reproduction environments, and require a separate decision before external disclosure or release.
What this announcement does not prove[source 1][source 2]
Anthropic’s research post reports results from an early validation exercise, but that sample is not a guarantee for a different repository, language or deployment. Model-generated findings remain fallible. Enrollment acceptance, scan cadence and actual reporting volume need project-specific confirmation. Rangoon has not established participation in this service, an adapter integration or a vendor endorsement.
Sources
Continue reading
Related reading
 News analysisAnthropic expanded AI for Science credits: preserve research evidence beyond access3 min read
 News analysisAnthropic released Petri for broad alignment audits, while its generated transcripts still needed human interpretation3 min read
 News analysisAnthropic donated Agent Skills to AAIF: treat open governance as a new supply-chain input3 min read