
OpenAI’s Admin plugin shows why conversation is not authorization
OpenAI introduced an administrative plugin for ChatGPT Work and Codex. Its permission-aware design highlights the need to preserve a before-and-after record around changes.
Historical reporting: OpenAI introduced the Admin plugin on August 25, 2026; Rangoon reviewed it on October 4, 2026.
 OpenAI
Key takeaways
- OpenAI described an admin interface for activity, groups, permissions, limits, and spending requests.
- A conversational request is an interface to an action, not an authorization grant by itself.
- Administrative evidence should record the requested change, effective permission, result, and resulting state.
What OpenAI announced[source 1]
On August 25, OpenAI introduced an Admin plugin for ChatGPT Work and Codex. OpenAI said the plugin can help administrators inspect workspace activity, manage members and groups, review effective permissions, and work with usage limits and spending requests through supported administrative actions.
OpenAI also says the plugin works within an administrator’s existing roles and permissions, mapping instructions to supported reads or writes and returning structured results. The announcement describes a permission-aware administrative interface. It does not mean ordinary conversational language bypasses workspace policies or that Rangoon has released an integration with the plugin.
Editorial analysis: conversation explains a change; authority permits it
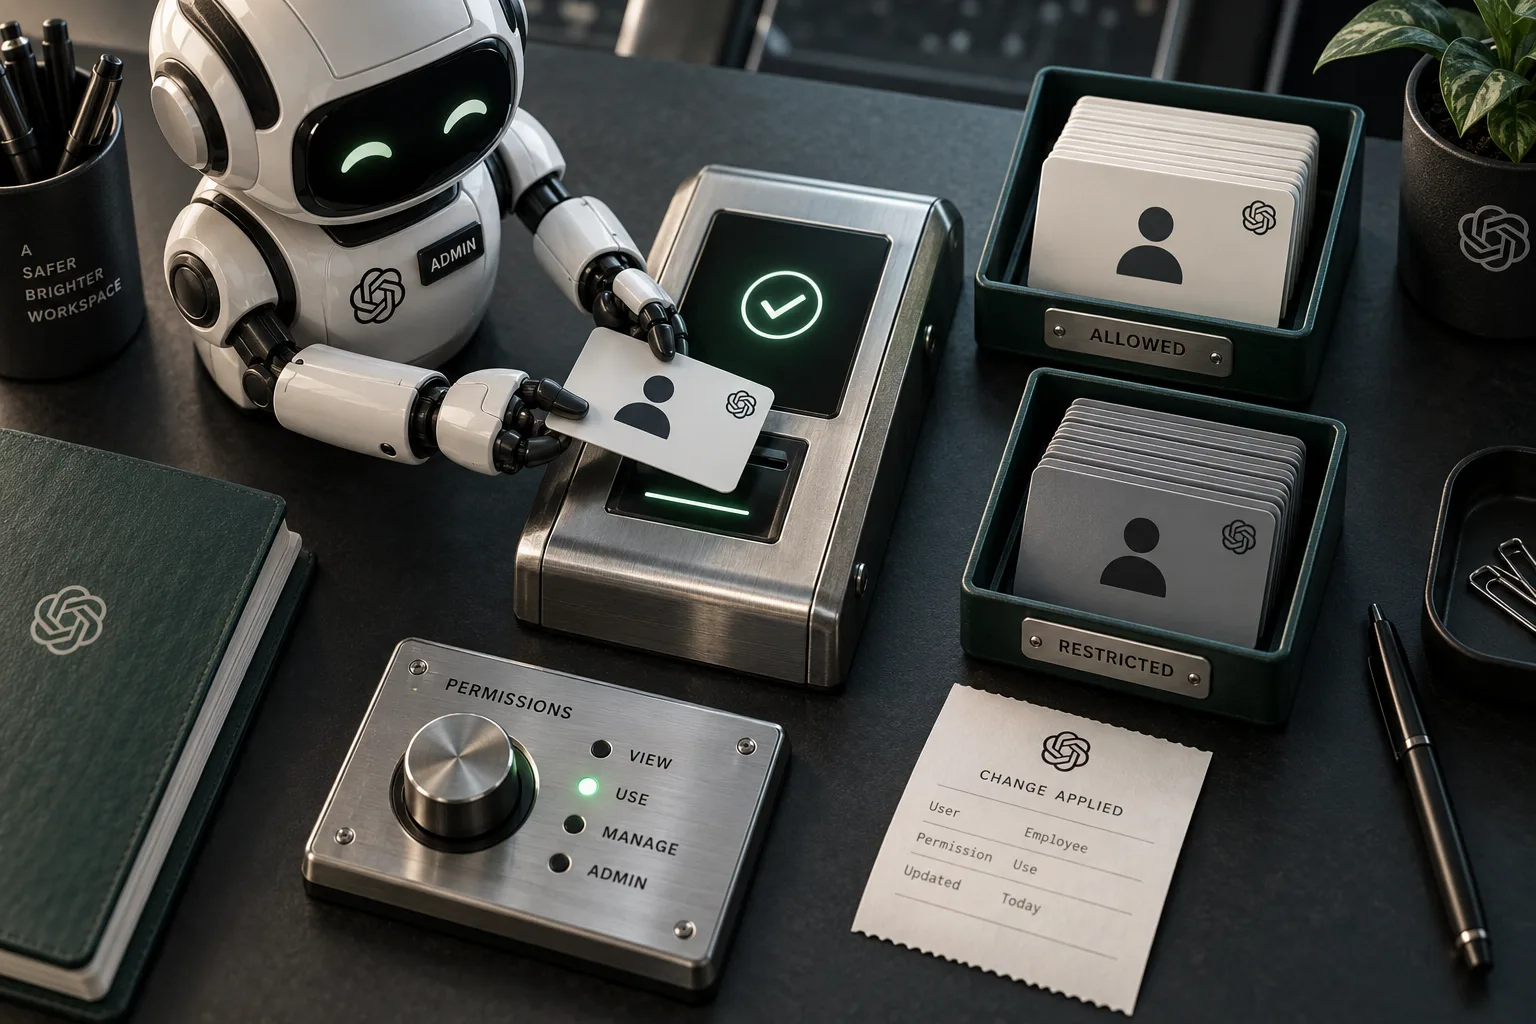
A conversational interface can reduce steps between an operator’s question and a supported administrative action. It should still leave the authorization boundary visible. The decisive facts are the authenticated actor, current effective permission, target workspace object, intended mutation, applicable approval requirement, and state returned after the operation. A clear sentence from an administrator does not make those facts optional.
For a permission change, useful evidence begins before the write. Capture target member or group, requested access change, initiating identity, effective permission evaluated, and any required review. Then capture action identifier, provider result, and a fresh read of resulting state. This before-and-after pair detects a partial application, changed target, or result that differs from requested scope.
A bounded engineering example uses a dry-run or preview where available, presents the exact permission delta for review, executes once, and reads back only target fields needed to confirm it. If confirmation fails or is ambiguous, the record should say so and avoid treating the change as settled. That is more useful than an unverified conversational acknowledgment.
- Bind the change to an authenticated actor and evaluated permission.
- Keep a concise before-and-after record for the affected object.
- Treat an unclear provider result as reconciliation, not success.
Integration and evidence boundary
Rangoon’s launch architecture distinguishes capability configuration from execution authority. It can represent a connector operation and required policy evidence, but the public site does not claim that Rangoon has released an Admin plugin connector, can administer a ChatGPT Work workspace, or inherits vendor permissions.
LNSAT’s reference path adds a narrower action-level control: it evaluates one operation, records required approval, creates a one-time authorization, and preserves a receipt. A conversational administration tool and authority engine address different layers. One can help an operator express a request; the other can bind the permitted action and evidence.
The durable practice is to retain both sides of the boundary: the interface record that shows what was requested and the authorization and readback record that shows what actually changed. That record also gives a later administrator a bounded basis for remediation without reconstructing intent from chat history alone.
Sources
- OpenAI: Introducing the Admin plugin for ChatGPT Work and Codex (August 25, 2026)
Continue reading